Prohack Wishes You a Very Happy New Year 2010

As 2009 goes by..

As 2009 ends I can only wish that 2010 may prove more productive,rejuvenating and brings all of you infinite reasons to cherish your life..2009 was a rocking year all together,the ups and downs may have seemed quite shaking,but we made through it and that’s why we are the most dominating species on this planet. Cheers up folks,lets make the coming year better than ever,by doing our best and believing in ourselves.Thanks a lot for supporting Prohack,Its your confidence in me that strives me to better every time.

A Very happy new year from Prohack.

Prohack wishes You a Very Happy New Year 2010 !!!

Also, you can celebrate your new year by purchasing merchandize like t-shirts,hoodies and more from Prohack at dirt cheap prices !!!! Check out the latest offerrings by visiting to the Prohack Store and support us..


XERO

[ I m having my final exam tomorrow so more or less,I will be busy tonight,but as soon as I get time, I will hangout with my friends,have some beer (fruit beer :P) and have some clan matches on counterstrike and Halo at my lair..I wish you were there :D ]


Posted by XERO . ALL RIGHTS RESERVED .

TOP 7 Must Read Articles at PROHACK – 2009 Reviewed

As 2009 goes away, its time to review what I did on PROHACK..and share the best of stuff with you folks again. I believeProhack - Your technology Navigator  these articles are a must read if you have been a regular here,and double if you are not. Prohack has gotten better with you guys and it was not possible without you..SO..Here are the Top 7 Must read articles at PROHACK -
Create a Zip Bomb of Deathuntitleddsa[13]
A zip bomb is usually a small file (up to a few hundred kilobytes) for ease of transport and to avoid suspicion. However, when the file is unpacked its contents are more than the system can handle.You can make your own zip bomb to annoy your friends or just out of curiosity (or wilderness) to experiment with it. Make sure you don't detonate it on yourself.
How to Hack Administrator from Guest Account Hack admin account from guest account
Ever wanted to hack your college pc with guest account/student account so that you can download with full speed there ? or just wanted to hack your friend’s pc to make him gawk when you tell your success story of hacking ? well,there is a great way of hacking an administrator account from a guest account by which you can reset the  administrator password and getting all the privileges an administrator enjoys on windows..Interested ?
Hack PHP 4.4 websites in 20 seconds Hack PHP 4.4 sites in 20 seconds
Actually sites with PHP 4.4 have a SQL injection vulnerability in them which makes their Admin control panel easily accessible,and I mean in one big shot,you will be admin of that site.
Top 10 Tips to optimize your website Top 10 web seo tips
Making a website is easy,but making it survive through the Wild Wild Web is quite a formidable task. I have seen many potential websites crumble and vanish through the web in a short span of time,and today I will be sharing my knowledge with you. I have followed the 10 simple rules which have allowed me to get the love of my readers in such a short time and have made ProHack more than a name in the web..Read them and follow them.
Top 10 Anticipated games of 2009Top 10 anticipated games of 2009
2009 proved to be a great year for gaming and the developers wants to keep the roller coaster ride of top releases keep going with extremely hyped games by the top dogs of gaming. The list is compiled on the factors on how much is known about the game,how incredible it looks the current user reviews,and the following big boys made it on the top 10 most anticipated games of 2009.
Hack LG KG195 for Increased Feature Hack LG KG 195
I used to have an LG KG195,an average mobile by LG electronics. A modest mobile with modest features,it has got Bluetooth, a basic media player and a VGA camera. However I soon got bored of this set and decided to tweak it to make it a more desirable device.Learn how to hack LG devices..
Top 10 LINUX speed hacksTop 10 Linux Speed hacks
As an extremely reliable Operating system, Linux  rarely needs to be rebooted. But when it does, it’s often slow to boot.Loads of Matrix style lines scrolling down the screen are sure to drive nuts added with boot time of GUI  initialization.. Fortunately, there are ways to speed things up. Some of these methods are not terribly difficult. (although some, unfortunately, are). Let’s take a look at Top 10 Speed hacks of Linux and let your linux box reincarnate with speed. 
Bonus -
Resident Evil 5 – An Honest ReviewRE5 - an Honest Review
Resident Evil 5 was one of the most hyped games of this generation and was prominently featured in various Top 10  Lists. The incredible amount of hype it generated was contributed to the long development period,the over the top gorgeous looking trailers,gory in game footage and just the plain curiosity,whether it will be able to surpass its legendary predecessor or not..
5 Type Of Virus Writers 5 Type of virus writers
Whilst stumbling on the net,I found this humorous description of 5 types of virus writers written by an actual hacker.I really loved the overall tone of the article and thought its worthy to share it with you guys..Enjoy.

Happy new year..

PS : Like this tutorial ? You can always support me by buying me a coffee or You can always try some of the cool merchandize from PROHACK.

Posted by XERO. All Rights Reserved.

How to Hack Nokia Phones – Remote DDOS Attack using SMS

Yep,One can hack Nokia phones by just sending a SMS,seems devilish isn't it? Although this vulnerability was found more than an year ago, I recently tried it and found it working in many sets. The Nokia S60 hacked -  rdhacker.blogspot.comvulnerability dubbed as “Curse of Silence” affects all Nokia Symbian 60/Series 60 devices and allows for remote SMS/MMS Denial of Service.One can send a specially crafted sms to lockup/crash any Series 60 device.

What is Required ?

  • MSISDN of the target.
  • A Mobile phone service provider which allows sending of SMS messages (Airtel in my case)
  • (Almost) any Nokia phone (or some other means of sending SMS messages with TP-PID set to "Internet Electronic Mail" )

Risk Levels

Although the vulnerability is spread across many versions of S60 platform,the Risk level is quite high for (for S60 2.6 and 3.0 devices)as upon attack,the target will not be able to receive any SMS or MMS messages until the device is Factory Resetted and Medium for S60 2.8 and 3.1 devices as upon Ddos attack,the target will not be able to receive any SMS or MMS messages while the attack is ongoing. After that, only very limited message receiving is possible until the device is Factory Resetted.

 The Series 60 N Series, E Series and some more phones can Be hacked - rdhacker.blogspot.com

The Attack

One can send an email using an sms by setting the messages Protocol Identifier to "Internet Electronic Mail" and formatting the message like this:

<email-address><space><message body>

The simplest attack will be -

123456789@123456789.1234567890123

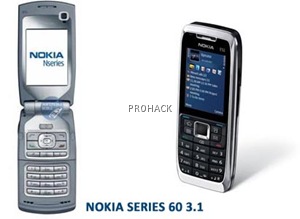
If such messages contain an <email-address> with more than 32 characters, S60 2.6, 2.8, 3.0 and 3.1 devices fail to display the message or give any indication on the user interface that such a message has been received. They do,however, signal to the SMS Career that they have received the message.Nokia Series 60 3.0 Prominent phones -  rdhacker.blogspot.com

Devices running S60 2.6 or 3.0 will not be able to receive any other SMS message after that. The user interface does not give any indication of this situation. The only action to remedy this situation seems to be a Factory Reset of the device (by entering "*#7370#" ) or using a Vulcan Death Grip.  Nokia Series 60 3.1 Prominent phones -  rdhacker.blogspot.com

Devices running S60 2.8 or 3.1 react a little different: They do not lock up until they received at least 11 SMS-email messages with an email address that is longer than 32 characters after that the device will not be able to receive any other SMS message and the phone will just display a warning that there is not enough memory to receive further messages and that data should be deleted first. This message is even displayed on an otherwise completely "empty" device.  Nokia Series 60 2.8 Prominent phones -  rdhacker.blogspot.com

After switching the phone off and on again, it has limited capability for receiving SMS messages again: If it receives a SMS message that is split up into several parts it is only able to receive the first part and will display the "not enough memory" warning again. After powercycling the device again, it can then receive the second part. If there is a third part, it has to be powercycled again, and so on.

Also, an attacker now just needs to send one more "Curse Of Silence" message to lock the phone up again. By always sending yet another one as soon as the status report for delivery of the previous message is received, the attacker could completely prevent a target from receiving any other SMS/MMS messages.

Only Factory Resetting the device will restore its full message receiving capabilities. Note that, if a backup is made using Nokia PC-Suite *after* being attacked, the blocking messages are also backuped and will be sent to the device again when restoring the backup after the Factory Reset.

Detailed List of affected phones

Tested on several S60 2.6, 3.0 and 3.1 devices. Since the vulnerable component is a S60 base functionality, it seems safe to assume that all devices with these OS versions are affected. I short if you own one of these,you are rounded unless u have a firmware upgrade/fix release by Nokia which fixes this attack.

S60 3rd Edition, Feature Pack 1 (S60 3.1)

  • Nokia E90 Communicator Series 60 Affected Devices - rdhacker.blogspot.com
  • Nokia E71
  • Nokia E66
  • Nokia E51
  • Nokia N95 8GB
  • Nokia N95
  • Nokia N82
  • Nokia N81 8GB
  • Nokia N81
  • Nokia N76
  • Nokia 6290
  • Nokia 6124 classic
  • Nokia 6121 classic
  • Nokia 6120 classic
  • Nokia 6110 Navigator
  • Nokia 5700 Xpress Music

S60 3rd Edition, initial release (S60 3.0)

  • Nokia E70
  • Nokia E65
  • Nokia E62
  • Nokia E61i
  • Nokia E61
  • Nokia E60
  • Nokia E50
  • Nokia N93i
  • Nokia N93
  • Nokia N92
  • Nokia N91 8GB
  • Nokia N91   
  • Nokia N80
  • Nokia N77
  • Nokia N73
  • Nokia N71
  • Nokia 5500
  • Nokia 3250

S60 2nd Edition, Feature Pack 3 (S60 2.8)

  • Nokia N90
  • Nokia N72
  • Nokia N70

S60 2nd Edition, Feature Pack 2 (S60 2.6)

  • Nokia 6682
  • Nokia 6681
  • Nokia 6680
  • Nokia 6630


Credits

Tobias Engel – The Original Vulnerability Founder

Tested and implemented on Airtel carrier using Nokia 3120 classic and N70/N73/E51 by XERO


Posted by XERO . ALL RIGHTS RESERVED.Source


Nokia N900 Review

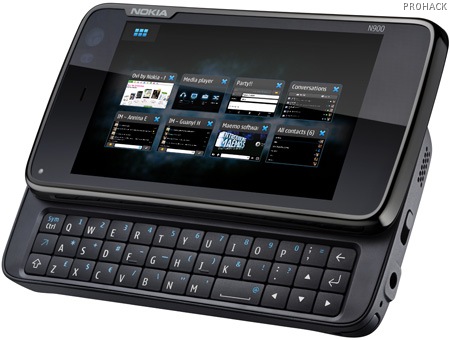
The market has been flurried by smartphones recently and Iphone stole the show by merging great looks with some really cool widgets and making it a must have. Losing its dominance over the Smartphone market,the Finnish mobile king Nokia tends to fight back by releasing N900.Earlier Nokia Smartphone came with home grown Symbian OS but this time Nokia has experimented by packing N900 with the stunning Linux distribution Maemo 5 which itself is a slimmed down version of Debian Linux and have added a host of top-end features, including a sizeable 3.5in touch screen, slide-out Qwerty keyboard, 5Mp camera with Carl Zeiss optics, Wi-Fi , A-GPS, quad-band and much more besides…
 Nokia N900
N900 is a beauty to behold and is chiseled to perfection (keeping in mind the fact that I tend to get sentimental everytime I see a cool gadget) and sports a sleek screen,black minimalistic looks and feels very pocketful.The keypad is quite tactile and responsive despite the small keys it sports.
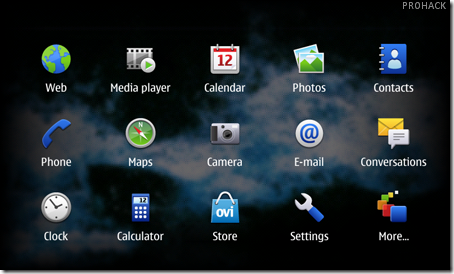
Maemo 5 looks quite similar to its Symbian predecessor and Nokia has made a promising move by moving on to open source Linux platform (3 cheers to Nokia).The Linux OS is powered by fast ARM Cortex A8 processor and Open GL ES 2.0 graphics and performs well by providing additional usability with a great user interface.
N900 Maemo 5 Interface
Frequent tasks like SMSing and Emailing is easy on N900 and it also supports Facebook widgets and sports a browser based on Firefox which is a good thing as it can handle multiple pages at once and updates them in real time.The camera takes surprisingly good pics owning to its Carl Zeiss optical lens and while it doesn't have a huge arrange of settings, it does offer macro, action and portrait modes, plus a dual LED flash, though there's no smile detection, timer or multi-shot options.
Nokia N900 front
Watching videos is a delight on N900,the 800X480 screen vivdly displays videos in amazing quality.Its supports major video formats and has a TV out option too.The Music player of  N900 is attractive and the phone itself is bundled with above average earphones. There is a basic FM which doesnt supports autotune. Also the phone supports onboard 32 GB memory and supports 16 GB external MicroSD card (just in case you are not satisfied by putting your entire audio collection on it). Call quality is good but the battery is a concern since owing its use of multimedia apps,it barely lasted a day on heavy use.
N900 is bundled with above average earphones
Final Verdict
Nokia N900 is a definitive phone if you have enough moolah to buy one.The Linux OS is solid,the interface intuitive at the end of the day,its a Nokia – the second name of quality (correct me if its wrong). Its a joy to use,a beauty to behold and the ultimate phone to flaunt to your friends.Nothing more..Nothing less.
Price in India – 650 $ , 500 EURO ,INR 34000/- approx

-XERO
You can also read N96 Review

PS : Like this article ? You can always support me by buying me a coffee or You can always try some of the cool merchandize from PROHACK.


Posted by XERO . ALL RIGHTS RESERVED.

IIS service vulnerability leaves users to attack

Another critical vulnerability have been found in the Microsoft IIS web service which allows malicious users to upload IIS service vulnerability leaves users to attackmalicious files by appending innocent filename extensions like “jpg” to malicious files. The problem arises from by the way Microsoft IIS parses file names with colons or semicolons in them which can allow attackers to bypass filters and potentially trick server into running a malware.

Soroush Dalili,the security researcher who found the flaw commented “ Impact of this vulnerability is absolutely high as an attacker can bypass file extension protections by using a semicolon after an executable extension such as '.asp,' '.cer,' '.asa' and so on," he continued "Many web applications are vulnerable against file uploading attacks because of this weakness of IIS."

Secunia,a Danish computer security service provider,confirmed the bug on a machine running a fully patched version of Windows 2003 R2 SP2 with Microsoft IIS version 6.

A Microsoft spokeswoman said company researchers are investigating the report. They are not aware of attacks targeting the reported vulnerability, she said.


Via The Registrar


POSTED BY XERO. ALL RIGHTS RESERVED.

Exams Over..Well Almost and I am Back :)

First of all a Very Merry Christmas friends..Sorry for a late update but I was having my final exams and was quite busy with them. Today they have been partially completed ( I mean I have just 2 exams left with ample time of 16 days to get hold of things in between ) and hence I m back with my techno-security babble. In the mean time I messed with my new cellphone ( A Nokia 3120 classic ),played Halo and decided to pursue RHCE and hanged out with girls :)

Ah well...Finally its over :)

Well I will be getting more time now with my blog and that’s a good thing,both for you loyal followers of PROHACK and for me :) cuz I have learnt much from this blog more than anything else.


Thanks for Being a Pro :)

XERO

POSTED BY XERO. ALL RIGHTS RESERVED.


Sorry Folks..Exams..No Computer and more

Its been a loooooong time since I have duked out something out of my mind,partly I don't have a motherboard and although my generous room mates allow me to surf net and play games, I just don't get into mood of posting out unless I m sitting on my machine. Further more,my end sems are there and I will be preparing for them. So, in short I will be back in late December or early January with a  new year full of more technobabble from yours only – Me :P

Awww...get me a new motherboard XD !

Till then..Have a nice time and keep your eyes open for more on Prohack.


Peace


XERO

Motherboard woes - Help me folks

Motherboard woes - Help me folks
Hi Folks..Sorry for a late post but I m very sorry to inform that My Motherboard (an Intel original D945GNT) has gone kaput and I m unable to post any articles any further until I get a new one.As usual I m on a hunt for a budget board (as cheap as possible,which will be able to give full bang for my buck) cuz I m low on moolah this month,I will be posting a full review on the board which I will select.
Also,You too can help me hunt for a new motherboard.

What I want is (or in formal language the specifications are :P ) -
  • Must be compatible with Pentium 4 3.0 Ghz HT pinless processor 530/630 (I have this processor now..and I m not willing to sell it :] )
  • Must support atleast Core2Duo processor (who knows I might need to upgrade :P).
  • Must contain Onboard graphics support (Nvidia/ATI preferred).
  • Must be in this range Rs /- 2700-3800 (4000 INR if exceptionally good).
You can comment or mail me at my email id - luckyelites@gmail.com

Thanks a lot friends.

Stay gold

-XERO

Tekken 6 – An honest review

Tekken has maintained its popularity since its advent without the need to reinvent itself.Tekken 6 – An honest reviewIts a game that speaks for itself.Well..The wait is over..Tekken 6 was released yesterday with all pomp and show and soon all the gaming press will flock on to review it.In the mean time I got my hands on a PS3 import and I decided to get my hands dirty and write an honest review about it...

Graphics - 8/10
If Tekken has one thing,its style which gives the game a distinct look and feel that forces the series to move to its roots without the need of reinventing itself.The game efficiently makes us gawk at the motion comic recaps in the story mode and  impressively rendered CGI sequences in the opening and ending movies..Tekken sports next-gen graphics engine under its hood and the game ran smoothly with no frame drops at all.

The CGI are excellent

The visuals are amazing and aesthetic,however I felt cheated when I felt that the character animations are recycled a bit which nevertheless are animated very well..The scenario campaign mode looks dated and I felt if I was duking out Godhand with a bit of updated graphics. Also some background sported stupid background scrolling which made me think if the stage was really moving..Overall its a huge upgrade of Tekken 5 on graphics front but there are some things which need to be reconsidered.Perhaps an expansion might sort it out.

Sound – 9/10

The music in Tekken 6 sets the overall mood for the fighting.The middle eastern,western,jazz and electronic;all are mingled very well to produce an awesome aural experience. the opening track and the CGI music is very well done.There is a certain series staple ‘thump’ sound associated with the hits which gives hitting someone in face an experience worthwhile.The tunes are catchy and I was forced to stop the match and to listen to the background music at times.Over all its well done.

Design - 8.5/10

Tekken 6 sets fan expectations quite high with the long development time and all the hype its associated with.The sequel boasts 40 characters to choose from and the ability to play online,the series has done its bit to remain competitive.In the standard offline mode,the game offers staple Practice Mode,the Story Mode in which you will battle and overtly powerful final boss Azazel,the ghost mashups that lets you battle AI opponents which simulate real world characters quite well and provide you a decent competition,the Time Attack and the Survival which will test your efficiency and record your personal best.With a second human player on side (as it happened with me) you can get into some serious vs battles.

Tekken 6 Character select

The Online play at the time of launch was quite poor with serious lag affecting the gameplay,as the strict timing needed for competitive gameplay is severely compromised and in some cases lag makes the game completely unplayable.The online mode also lets you download ghost data for your personal use and for your ranked and unranked matches.

Tekken 6

The game includes a scenario campaign mode that's an entirely a different game altogether,like the Tekken Force mode in the original Tekken 3 but the incompetent camera and the bad implementation of moveset in the campaign can make your experience sour.

Gameplay – 9/10

Tekken embraces both the newcomers and the series veterans with open arms and you will have plenty of fun all together as long as you will be matching up against opponents of your level.The 4 button fighting scheme may seem deceptively intuitive to the players,but it needs skill and the right timing to keep the attacks flowing and be in the groove.Mixing up the throws,the high and low attacks,sidestepping all gives you a tactical advantage against the opponent,but simply mashing up buttons and hoping for the best is fun too. The game heavily emphasizes combos for massive damage and puts emphasis on bounding moves,which means to slam opponents on the ground and then attack using appropriate moves at specific time to keep the low juggle going on.

Tekken 6 juggle

The matches move on too quickly and the game features a rage system which means the game gives player a last boost of attack power when his health is low to change the face of match.The game has a 3d fighting experience of its own and overall its just another Tekken at heart.


Last word

Like MGS4,Tekken 6 is a love it or hate it type of game.When you will fire it up,you will probably already know how it

Tekken 6

will strike you and the series has already maintained a good following for good reasons.In the end,even if the extras provided are not worth in gold,they still add a good value to the overall package.Tekken 6 is just Tekken 6 nothing more,nothing less.

Final Score – 34.5/40


POSTED BY XERO . ALL RIGHTS RESERVED.

Google Spanner – A better Google

A recent presentation confirmed the existence of the proprietary distributed technology that will automatically move untitledand replicate the load between Google’s mega data centers when traffic and hardware issues arise. Perhaps this was  done to counter the issues of lagtime when Gmail was down..who knows? The platform is known as Spanner.

Google fellow Jeff Dean hinted about Spanner in the classic Google manner during a conference this summer and has now confirmed its existence in a presentation (PDF) delivered at a symposium earlier this month. .Dean’s presentation calls it a “storage and computation system that spans all our data centers [and that] automatically moves and adds replicas of data and computation based on constraints and usage patterns.” This includes issues and constraints related to bandwidth, packet loss, power, resources, and “failure modes”.

Google Spanner

Google is intent on scaling Spanner to between one million and 10 million servers, encompassing 10 trillion (1013) directories and a quintillion (1018) bytes of storage. And all this would be spread across “100s to 1000s” of locations around the world.

Thats a hell lot of data and power granted to a single corporation which will be housing an exabyte of the world's data across thousands of custom-built data centers.

Lets see how this unfolds..


POSTED BY XERO. ALL RIGHTS RESERVED.Source

Microsoft addon blocked by Firefox

Last Friday Mozilla blocked one of Microsoft’s sneaky addons that put end user security at stake.The addon,dubbed as the usual suspect...".NET Framework Assistant" and a plug-in named "Windows Presentation Foundation" -- have been blocked by Mozilla  as a precautionary measure, said Mike Shaver, the company's head of engineering.These addons installed without any permission and may be manipulated by malicious users to code their way into the browser and infiltrate the system(Who knows a botnet may be well under a way..anyway?),even their Internet Explorer 8 had the same built in flaw.The addon was notable for its annoying removal and had been infiltrating firefox since Microsoft pushed them out with the .NET Framework 3.5 Service Pack 1 (SP1) update in February this year.Until or unless some registry hacking was employed,this addon was impossible to remove entirely.As the folks at Mozilla cant fix the software,the safest way they can go on with was to block it,which they already did on Friday.

Later Microsoft released a patch which will counter the vulnerability,you can download it here.

Mozilla have been aggressive for the security for their users and have been making sure that 3rd party addons are secure and will enforce it more effectively with the release of Firefox 3.6 (Beta slated to be released on wednesday) which will actively notify user when they will visit a site which relies on vulnerable and outdated addons.


POSTED BY XERO . ALL RIGHTS RESERVED.

Diwali Celebrations and Home coming

Happy DiwaliFriends..The festival of light is knocking as usual and its time for some grand celebrations at home.I will be leaving today for Ambala, leaving my room and my beloved mean machine and all of techs to have some peace and to light some crackers :P . Diwali holds some of the most special moments for me in my life,and symbolises the victory of Good over Evil as in mythology,and some old grand reunions of friends at our favorite hangouts.Its been some time when since I have had a vacation..I will be getting back into old streets of Ambala,decorate my home till it shines the most (literally),light diya’s, feast on sweets and play pranks on my friends..
May this Diwali bring endless pleasure,happiness and peace to all of you and may it rejuvenate all of us to live life like it is meant to be.
A very Happy Diwali once again.
I will be back on Monday and will resume to my daily caricature of technology.


PROHACK wishes you a very Happy Diwali  !!!
I hope you will enjoy it as much as I do..
Cheers

Rishabh Dangwal

POSTED BY XERO . ALL RIGHTS RESERVED.

Russia Blamed with Cyberattack on Poland

Leaked details by the Polish newspaper Rzeczpospolita indicate a large but unsuccessful attack on Polish Government systems which originated in Russia last month.The details indicate that the attack coincided with the 70th anniversaryCyber Crime news of the outbreak of World War Two and was coordinated at the same time when Russian President Vladimir Putin visited Poland.

The attack might have been referenced to the anniversary of infamous invasion of Poland by Nazi Germany and the Soviet Union on September 1939 under the secret terms of the Molotov–Ribbentrop non-aggression pact,however its still unclear as actual reason have not surfaced..yet.

Russia has been in news as the disputes between Russia and its neighbors have made their way over the Internet in recent years. and For example, Russian Hackers have been quite nefarious over cyberattacks at Georgia last year and security researchers subsequently blamed the attacks on civilians and Russian cyber-crime gangs.

The Internet infrastructure of Estonia was ripped apart in April 2007, following a dispute over the relocation of Soviet-era war memorials and graves.


Via The Registrar


POSTED BY XERO . ALL RIGHTS RESERVED.


Ethical Hacking and Security Classes – Begin With Basics

Newspaper insert
The security scene at India is quite ugly,according to a survey,a whopping 97% of computer users are pretty ignorant when it comes to computer security Folks,last time I mentioned about the classes's on Ethical Hacking and Security which are going to be held at Rajpura as of now. The course Fee has been discounted to a mere 1500/- INR for Indian citizens (75 USD for foreign citizens) for the inauguration batch.The course will be covering from the ground zero of security and its basics.The course duration will be 16 hours and will be held at weekends 2 hours each to complete it in 1 month.
You can contact me using the contact form provided here

Keep learning

POSTED BY XERO . ALL RIGHTS RESERVED.

7 Must Have Tools For Every Hacker

Its been a while since I have posted about some hacking tools and with increasing number of emails asking me to do an  7 Must Have Tools For Every Hackerarticle on it,I finally decided to cover it up.Hacking tools are developed by some really good coders out there to ease out many complex tasks which have to be done manually and took painstakingly great deal of time and effort.All these tools provided here are free of cost,are tried hands on and are being actively developed by community,and if not,their alternatives are provided.To summarize it up,these are the 7 must have tools for every hacker out there.
1. Nmap
I think everyone has heard of this one, it recently had a version 5 release.
Nmap (Network Mapper) is a free open source utility for network exploration or security auditing. It was designed to Nmap rapidly scan large networks, although it works fine against single hosts.Many systems and network administrators also find it useful for tasks such as network inventory, managing service upgrade schedules, and monitoring host or service uptime. Nmap uses raw IP packets in novel ways to determine what hosts are available on the network, what services (application name and version) those hosts are offering, what operating systems (and OS versions) they are running, what type of packet filters/firewalls are in use,and dozens of other characteristics. It may be used to discover computers and services on a computer network, thus creating a "map" of the network.Nmap runs on most types of computers and both console and graphical versions are available. Nmap is free and open source.Can be used by beginners (-sT) or by pros alike (packet_trace). A very versatile tool, once you fully understand the results.
Download Nmap
Also,You can learn how to perform a simple Nmap scan by reading this article.
2. Nessus Remote Security Scanner
Recently went closed source, but is still essentially free. Works with a client-server framework.Nessus is the worlds  Nessus Remote Security Scanner most popular vulnerability scanner used in over 75,000organizations world-wide. Many of the worlds largest organizations are realizing significant cost savings by using Nessus to audit business-critical enterprise devices and applications.
Download Nessus
3. Wireshark
If you have been reading my site,you might have read about it in a couple of articles.Wireshark is a GTK+-based  Wiresharknetwork protocol analyzer, or sniffer, that lets you capture and interactively browse the contents of network frames. The goal of the project is to create a commercial-quality analyzer for Unix and to give Wireshark features that are missing from closed-source sniffers. Works great on both Linux and Windows (with a GUI), easy to use and can reconstruct TCP/IP Streams! .
Download Wireshark
4. Cain and Abel
The swiss knife of hacking tools..Cain & Abel is a password recovery tool for Microsoft Operating Systems. It allows easy recovery of various kind of passwords by sniffing the network, cracking encrypted passwords using Dictionary, Brute-Force and Cryptanalysis attacks, recording VoIP conversations, decoding scrambled passwords, revealing password boxes, uncovering cached passwords and analyzing routing protocols.The program does not exploit any software vulnerabilities or bugs that could not be fixed with little effort.
Download Cain and Abel
5. Kismet
Kismet is an 802.11 layer2 wireless network detector, sniffer, and intrusion detection system. Kismet will work with  Kismetany wireless card which supports raw monitoring (rfmon) mode, and can sniff 802.11b, 802.11a, and 802.11g traffic. A good wireless tool as long as your card supports rfmon
Download Kismet
6. NetStumbler
Yes a decent wireless tool for Windows! Sadly not as powerful as it’s Linux counterparts, but it’s easy to use and has a NetStumbler nice interface, good for the basics of war-driving. NetStumbler is a tool for Windows that allows you to detect Wireless Local Area Networks (WLANs) using 802.11b, 802.11a and 802.11g. It has many uses:
  1. Verify that your network is set up the way you intended.
  2. Find locations with poor coverage in your WLAN.
  3. Detect other networks that may be causing interference on your network.
  4. Detect unauthorized rogue access points in your workplace.
  5. Help aim directional antennas for long-haul WLAN links.
  6. Use it recreationally for WarDriving.
Download NetStumbler
7. SuperScan
Powerful TCP port scanner, pinger, resolver. SuperScan 4 is an update of the highly popular Windows port scanning tool, SuperScan.If you need an alternative for nmap on Windows with a decent interface, I suggest you check this out, it’s pretty nice.
Download Superscan
Alternatively,you can try Angry IP Scanner which is a pretty good replacement for it.

You might also want to read about -
5 hacking sites for budding Hackers
Top 10 Must read articles at Prohack
Top 10 linux Speed hacks
5 Myths about Safe Surfing


Stay Gold and keep learning.

PS : Like this article ? You can always support me by buying me a coffee or You can always try some of the cool merchandize from PROHACK.


POSTED BY XERO . ALL RIGHTS RESERVED.
Twitter Phishing at its best

Botnets..Ddos..and Now Phishing..

Yup,everybody’s favorite microblogging service Twitter is now under a phishing attack.Recently,Twitter has been Twitter Phishing at its bestnotoriously attacked by malicious hackers worldwide,It was uncovered recently that it was being used as a Botnet Control Channel, shortly before that it was subjected to a DoS attack. Phishers are now targeting Twitter users in a new attack which involves sending direct messages to Twitter users which contain a link to a site requesting usernames and passwords.

As usual..once the attackers have that, they can take over the account of the victim and use it to send out more messages. However..I’m not exactly sure why the hell anyone would want to steal Twitter accounts?

Possibilities -

  • To monetize them by sending tweets using those accounts in order to spam and spam some more about referrals and affiliate schemes.
  • Perhaps in future tweeting a link to a virus site which might lead to outbreak of a new virus like Conficker.
  • Just for fun’s sake..duh

The cornerstones of social engineering in phishing attacks after all humans are the weakest link in the chain of security.

If you are using Twitter you should follow @spam and keep up to date with what is happening on the network.


In the mean time,You can Join Prohack at Twitter


Keep Learning


POSTED BY XERO . ALL RIGHTS RESERVED.


Secure your Web tech using Websecurify

With lots of application testing frameworks like Acunetix and Saint available,its quite difficult to make a mark in the Websecurifysecurity market,however when it comes to secure your web technologies,Websecurify does a pretty good  job.Websecurify is a web and web2.0 security initiative specializing in researching security issues and building the next generation of tools to defeat and protect web technologies. 

Key Features

JavaScript – Websecurify Security Testing Framework is the first tool of its kind to be written entirely in JavaScript using only standard technologies adopted by the leading browsers.

Multiple Environments – The core technology can run in normal browsers, xulrunner, xpcshell (command line), inside Java or as part of a custom V8 (Google Chrome‘s JavaScript Engine) build. The core is written with extensibility in mind so that more environments can be supported without changing even a single line of code.

Multi-platform – The tool is available and successfully runs on Windows, Mac OS, Linux and other operating systems.

Automatic Updates – Every single piece of the tool is subjected to automatic updates. Secure your Web tech using Websecurify - rdhacker.blogspot.comThis means that newer and more advanced versions of the tool can be shipped to your front door without you lifting your finger. This however is completely optional. The automatic update can be turned off if needed.

Extensions – Because the tool comes wrapped in xulrunner by default (keep in mind that we can support any other JavaScript environment) we benefit from all cool features that Firefox has, such as extensions. Extensions are easy to write and maintain and can customize every single aspect of the tool and there are already tones of resources and documentation, including books and what not, out there to teach you exactly how to do that. We will be providing documentation as well.

You can download Websecurify 0.3 here:

  1. Windows
  2. Linux
  3. Mac

The official blog claims to have a pro version in pipeline which looks promising too.


Posted by XERO . ALL RIGHTS RESERVED.


LYNX - Surfing Internet the Old School way

Internet Browsing has changed a great deal in the past 15-20 years,I remember getting my hands on Internet Explorer 4.0 in late 90’s when I was a small kid (I was a not-so-stupid kid :P) .I was in retro mood last week,and being a LYNX - Surfing Internet the Old School way - rdhacker.blogspot.com dedicated netizen,I spent hours and hours on reading wikis and researching about the web browsers. Being curious, I later installed Windows 95 to get an authentic look and feel of web browsing in retro way and got my hands on Internet Explorer 1.0 and Netscape Navigator. It was fun..but I got bored soon :P

Sill later while I was surfing on Backtrack 3 through Mozilla Firefox, I became quite curious about the text based browsers,and voila,I got my hands on Lynx – the great grand father of all the web browsers available today. The brainchild of the folks at University of Kansas,Lynx became publicly available in 1993, around the same time browsers such as Mosiac and Cello were released.

The most popular browsers today include Firefox 3, Opera, Safari, and Google Chrome,Internet Explorer (?) but Lynx has retained a solid share.Google tests and certifies its webs pages and results LYNX compatible and experienced SEO guru’s will tell you to test your website on Lynx for checking its visibility and usability online.Basically, if you want to make sure your high tech website can be fully crawled by very basic search engine bots and crawlers, Lynx does an excellent job. Website designers often fire up a Lynx browser to make sure that people who surf the web with images turned off can still navigate their sites.

here is PROHACK running on lynx -

Yep..Thats PROHACK on Lynx :) pretty cool huh ?

However..Because lynx does not support graphics, web bugs that track user information are not sent, and emails can be read without the invasion of privacy of HTML enabled web browsers. So that means lynx offers better security if you run it under a good environment ( and if you are nerd enough to use it :P ).

Lynx does support HTTP cookies, which can be used to track user information. But like most browsers, cookie support can be disabled.

The best part..Yep..You guessed it right - Lynx is free under GNU GPL. What else a geek want..

You can get retro too and Download Lynx from here -

Download Lynx


K33p L34rning


POSTED BY XERO. ALL RIGHTS RESERVED.

Rabid Neurosis Takedown – Pirates Busted

Seems like the decade is proving hard for the black hats,pirates and phishers are busted down by the eminent feds for some serious jailtime. The spree continues when Rapid Neurosis,better known as RNS in the late 90’s/early 2000s RNS is no more... - rdhacker.blogspot.com scene was stung by the whip of law.Six men have been accused of running one of the world’s most prolific music piracy ring, an online crew federal prosecutors allege delivered more than 25,000 copyrighted albums, often before they were officially released.RNS was quite popular in the scene with the group releasing more than 25000 music albums on P2P. RNS occasionally used the tagline "Rabid Neurosis - Spread The Epidemic.".RNS was sometimes believed to have started the mp3 scene. After their group was mentioned in an MTV News article about the early leak of the Eminem album Encore, RNS stopped including their initials in filenames and ID3 tags.They stopped around 2007 though, I guess that’s when Bit Torrent and p2p was really taking off.
With the demise of popular clans (remember aXXo ? anyone?) I am beginning to wonder if the scene is being ripped out of itself.
25,000 albums is a serious number and I bet they will be fined ridiculously.
The next bet for the aftermath - 6 more people filling for bankruptcy.
They had an impressive network of contacts with people from retail outlets, cd printing factories and radio stations. All the people who get tracks and whole albums before they hit the streets.
Are the days of h4x0r5 over ?

Update - Houston Jury Finds Member of World's Largest Alleged Internet Music Piracy Group Not Guilty
You can read more @ http://www.earthtimes.org/articles/show/houston-jury-finds-member-of,1214284.shtml

 -
POSTED BY XERO .ALL RIGHTS RESERVED.