Tested it on test firewalls and it works like a charm : )
https://packetstormsecurity.com/files/136430/Fortigate-Backdoor-Password-Calculator.html
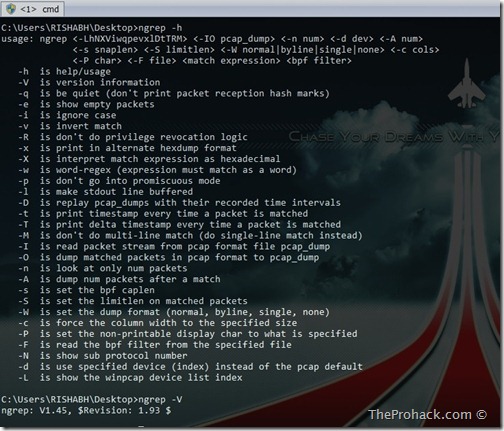
We have got a lot of packet sniffer/analyzer software out there, I am a self confessed Wireshark & Ettercap lover, but still, when it comes to analyzing network traffic from command line in a fast manner, ngrep is my one of my favourites. Written by Jordan Ritter its used to “grep” traffic patterns from the network interfaces. As per official documentation -
ngrep is a pcap-aware tool that will allow you to specify extended regular or hexadecimal expressions to match against data payloads of packets. It currently recognizes IPv4/6, TCP, UDP, ICMPv4/6, IGMP and Raw across Ethernet, PPP, SLIP, FDDI, Token Ring and null interfaces, and understands BPF filter logic in the same fashion as more common packet sniffing tools, such as tcpdump and snoop.
ngrep runs on Windows & *nix platforms alike and you need WinPCAP to run it since it relies on it.
Once you install it, it by default uses the first interface on your machine, so , make sure to check the detected interfaces by running -
C:\Users\RISHABH\Desktop>ngrep -L
idx dev
--- ---
1: \Device\NPF_{4D491111-D331-42BC-9A33-98EF8C40D422} (Microsoft)
2: \Device\NPF_{ADBF6AC1-D111-463D-8D99-C58FA1BEF979} (Sun)
3: \Device\NPF_{6F801AE0-CA61-4A6D-B5FF-DCB7CE8FC529} (VMware Virtual Ethernet Adapter)
4: \Device\NPF_{930B6EC8-A5E3-4FFA-B68F-F159FDFC2064} (VMware Virtual Ethernet Adapter)
5: \Device\NPF_{D1999293-A041-4C2A-B63F-5D8B4906000F} (Realtek PCIe GBE Family Controller)
exit
Now for example you want to check out whats going on at port 23 using interface 5
C:\Users\RISHABH\Desktop>ngrep -d 5 port 23
interface: \Device\NPF_{D1999293-A041-4C2A-B63F-5D8B4906000F} (192.168.1.0/255.255.255.0)
filter: (ip or ip6) and ( port 23 )
exit
0 received, 0 dropped
Piece of cake.. and if you want to filter any website in you are searching for keyword "password" then :
ngrep -d 5 “password” port 80
Easy aint it ? Ngrep does it all : ] With some complex grep commands , you can become a pcap ninja.
Well, you can


 applications. Once it detects one or more SQL injections on the target host, the user can choose among a variety of options to perform an extensive back-end database management system fingerprint, retrieve DBMS session user and database, enumerate users, password hashes, privileges, databases, dump entire or user’s specified DBMS tables/columns, run his own SQL statement, read or write either text or binary files on the file system, execute arbitrary commands on the operating system, establish an out-of-band stateful connection between the attacker box and the database server via Metasploit payload stager, database stored procedure buffer overflow exploitation or SMB relay attack and more.Enthusiastics can experiment with its opotions and pwn many of the servers around,or can test their skills to secure their servers..but remember,SQL map is a tool,its might help you to find and apply vulnerabilities and injections,but in the end,you really must have a good knowledge of SQL some real pwning out there..
Linux Source: sqlmap-0.7.tar.gz
Windows Portable: sqlmap-0.7_exe.zip
Hi friends.. I recently bought HTC wildfire and have been experimenting with it to the fullest. 
G-mon

G-mon is a powerful WarDriving scanner and GSM / UMTS Netmonitor and drive test tool. It scans for all WiFi networks in range & saves the data with GPS coordinates into a file on your sd card. You can create a kml file for Google Earth. It shows you the encryption, channel an signal strength. It shows all APs in range in a live map. I used it to collect lots of wifi data which I will be publishing soon.
Wardrive

another fantastic wardriving app which stores scans in sqlite db on the sdcard and displays found networks around in the map.It Requires Google MAPS installed.
Wifi Analyzer

This app literally turns your android phone into a Wi-Fi analyzer!! It helps you to find a less crowded channel for your wireless router and allows to audit networks.
Once you get networks, you can then break them into it using Aircrack and backtrack. Its easy and worth its salt :) . Here is a slice of my wardriving logs while i was in DTC bus :D
BSSID;LAT;LON;SSID;Crypt;Beacon Interval;Connection Mode;Channel;RXL;Date;Time
00:08:5C:EF:08:F0;28.56602;77.22951;Adiva;WpaPsk;-93;Infra;11;-92;2011/03/17;18:52:01
00:08:9F:81:8F:C4;28.56944;77.20531;Car0baR;WPA2;-96;Infra;6;-95;2011/03/17;18:58:30
00:0F:A3:6A:88:B8;28.56804;77.22473;sbi;Wep;-93;Infra;6;-91;2011/03/17;18:53:02
00:17:9A:09:D1:79;28.56813;77.22440;WebunivM;Wep;-93;Infra;6;-91;2011/03/17;18:53:05
00:18:02:87:02:8F;28.56845;77.22306;RT2561_6;Wep;-94;Infra;6;-93;2011/03/17;18:53:18
00:18:02:8E:32:5A;28.56885;77.21437;SrDDGA;WpaPsk;-91;Infra;6;-90;2011/03/17;18:55:31
00:18:02:92:A2:73;28.56955;77.20365;mtnlbb;Wep;-90;Infra;6;-89;2011/03/17;19:00:21
00:18:39:AA:5E:B8;28.56845;77.22306;Neeta;Wep;-89;Infra;11;-88;2011/03/17;18:53:18
at the end of the day, the moment that put a smile on my face was when i saw this as a network name near Delhi Cantt -
“You cant hack this Wifi dear neighbor”
It was a wpa2/psk secured network with static ip and mac filtering and the guy knew what he was doing :) Watching secured networks always makes my day.
Mausezahn is a free fast traffic generator written in C which allows you to send nearly every possible and impossible packet. It is mainly used to test VoIP or multicast networks but also for security audits to check whether your systems are hardened enough for specific attacks.
Mausezahn can be used for example:
Mausezahn is basically a versatile packet creation tool on the command line with a simple syntax and context help. It could also be used within (bash-) scripts to perform combination of tests. By the way, Mausezahn is quite fast; when started on my old PIII-Laptop (1.4 GHz, Gigabit Ethernet) I measured 755 Mbit/s using the interface packet counters of an HP ProCurve 5400 switch.
Currently Mausezahn is only available for Linux platforms. Please do NOT PORT Mausezahn to Windows! (Here is a nice explanation why; I really share Felix von Leitner’s point of view.)
Yoiu can download Mausezahn here:
Or read more here.
Like This post ? You can buy me a Beer :)
If you are in security, you might have heard of an Intrusion Detection system, which is a device or mechanism that 
Snort can be run in 4 modes:
A lot of people in the very active snort community are sharing their security rules which is very useful if you are not an security expert and wants to have up-to-date rules.Snort can be combined with other free software such as sguil, OSSIM, and the Basic Analysis and Security Engine (BASE) to provide a visual representation of intrusion data..which is in fact a PHP script displaying alerts on a web interface. At the end of the day, Snort is a must have for any security researcher or network paranoids out there..another mentionable IDS systems are Fragrouter,OSSEC HIDS and sGUIL.
You can download Snort from here
Like This post ? You can buy me a Beer :)
Posted by XERO. ALL RIGHTS RESERVED.
 testing and breaking program available. JTR, as its fondly called ,combines multiple password cracking packages into one package,includes auto detection of hashes and is a fast password cracker. It is currently available for many flavors of Unix, Windows, DOS, BeOS, and OpenVMS and supports 15 different platforms . Its primary purpose is to detect weak Unix passwords ( no..I m kidding,Its primary purpose is to break passwords :P ).It can natively detect and crack various encrypted password formats including several crypt password hash types most commonly found on various Unix flavors (based on DES, MD5, or Blowfish), Kerberos AFS, and Windows NT/2000/XP/2003 LM hash. JTR has an active community and multiple third party patches have been added to increase its functionality to include MD4-based password hashes and passwords stored in LDAP, MySQL and others unsupported hashes. JTR is the penultimate when it comes to password cracking in windows (Cain and Abel is the ultimate :P), but for Linux and open source,its the best you can get your hands on.Fire it up with a wordlist and you are good to go
root@0[john-1.6.37]# cat wpass.txt
user:AZl.zWwxIh15Q
root@0[john-1.6.37]# john -w:password.lst wpass.txt
Loaded 1 password hash (Traditional DES [24/32 4K])
example         (user)
guesses: 1 time: 0:00:00:00 100% c/s: 752 trying: 12345 - pookie
You can download JTR from here
 (DVWA) is great application to plunge yourself in.DVWA is a PHP/MySQL web application that is damn vulnerable..literally. Its main goals are to be light weight, easy to use and full of vulnerabilities to exploit and it successfully achieves those :P . And frankly it can be used to learn or teach the art of web application security.
Wireshark is the world's foremost network protocol analyzer, and is the de facto (and often de jure) standard across many 
Wireshark was written by networking experts around the world, and is an example of the power of open source. It runs on Windows, Linux, UNIX, and other platforms. 
Wireshark was previously known as Ethereal. The name might be new, but the software is the same. Wireshark's powerful features make it the tool of choice for network troubleshooting, protocol development, and education worldwide.
Posted by XERO . ALL RIGHTS RESERVED.
Hiren's BootCD is an all in one Dos Bootable CD, which consists of extremely essential tools for your system in case of 
Posted by XERO . ALL RIGHTS RESERVED.
Net Tools is a comprehensive set of host monitoring, network scanning, security, administration tools and much more, all with a highly intuitive user interface. It's an ideal tool for those who work in the network security, administration, training, internet forensics or law enforcement internet crimes fields. Net Tools is mainly written in Microsoft Visual Basic 6, Visual C++, Visual C# and Visual Studio .NET. 
Net Tools is cutting-edge security and network monitoring software for the Internet and Local Area Networks, providing clients with the ability and confidence to meet the challenges of tomorrow's technology. Keeping pace with the industry trends, we offer professional tools that support the latest standards, protocols, software, and hardware for both wired and wireless networks. Net Tools is a very strong combination of network scanning, security, file, system, and administrator tools useful in diagnosing networks and monitoring your PC and computer's network connections for system administrators. Next to the essential core tools it includes a lot of extra valuable features. It’s a Swiss Army knife for everyone interested in a set of powerful network tools for everyday use. This all-in-one toolkit includes also a lot of handy file and system utilities next to the huge amount of network tools. The menus are fully configurable, so in this way you won’t get lost in the extremely large amount of essential tools. All the additional features will make this application a must have for all system Administrators. There are numerous constructive and valuable applications included in Net Tools that can be used for a great amount of purposes. The latest version of Net Tools is hybrid; it means that it’s capable of working together with applications that are made and designed for Net Tools, so in this way more flexibility and user-friendliness is obtained. This software is designed for the Microsoft Windows OS (Windows 98, NT, 2000, 2003, XP, Vista). It’s entirely compatible and has thoroughly been tested on Windows XP. With the 175+ tools it is a great collection of useful tools for network users. The size of Net Tools 5.0.70 is approximately 25 Mb. 
Net Tools 5.0 (build 70) contains a whole variety of network tools.
Download Net Tools 5.0 build 70 from Mabsoft
Cheers and Keep learning.
Posted by XERO . MABSOFT . ALL RIGHTS RESERVED .


Hardware Information
Software Information
Security
Diagnostics
Reporting
New features in EVEREST version 4.50
Overall,its an indispensible tool for a system analyst and hardware as well as software engineers for benchmarking and comparing the performances of various components of PC.
Download Everest Ultimate Edition
posted by XERO . ALL RIGHTS RESERVED .
 Nmap ("Network Mapper") is a free and open source (license) utility for network exploration or security auditing. Many systems and network administrators also find it useful for tasks such as network inventory, managing service upgrade schedules, and monitoring host or service uptime.Nmap is a security scanner originally written by Gordon Lyon (Fyodor). It may be used to discover computers and services on a computer network, thus creating a "map" of the network. Just like many simple port scanners, Nmap is capable of discovering passive services on a network despite the fact that such services aren't advertising themselves with a service discovery protocol. In addition Nmap may be able to determine various details about the remote computers. These include operating system, device type, uptime, software product used to run a service, exact version number of that product, presence of some firewall techniques and, on a local area network, even vendor of the remote network card.
Nmap runs on Linux, Microsoft Windows, Solaris, and BSD (including Mac OS X), and also on AmigaOS.Linux is the most popular nmap platform and Windows the second most popular.
Nmap uses raw IP packets in novel ways to determine what hosts are available on the network, what services (application name and version) those hosts are offering, what operating systems (and OS versions) they are running, what type of packet filters/firewalls are in use, and dozens of other characteristics. It was designed to rapidly scan large networks, but works fine against single hosts.
Nmap is ...
Features
Typical uses of Nmap:
Modules and libraries utilizing Nmap:
Nmap's preferred output format is XML, which comes in handy for interpreted languages because they can parse and present this information for use by users' scripts.
Posted by XERO Excerpts form Nmap site and wikipedia

Dark Mailer is a super fast bulk email software that sends out at speeds greater than 50,000 emails per hour on a dedicated mailing server. Dark Mailer has the capability to use Proxies and Relays and also to send directly. Some of the features include:
The software taps into a network of zombie computers and is able to send 50,000 e-mail messages per hour from a regular cable modem connection. It affords near-total anonymity because of the networking and is often used by spammers. It currently does not have an official website for downloading.
Robert Soloway, one of Internet's biggest spammers, used it. On July 23, 2008, the 29-year-old Solway was sentenced to nearly four years in prison and ordered to forfeit more than $708,000 in income. Prosecutors had asked for a 9-year sentence. He has also lost civil suits for spamming, and owes civil penalties totaling more than US $17 million.
Note: Some Antivirus classified this as hack.tool or Mass.flooder
Posted by XERO .
MSN Chat Monitor And Sniffer
MSN Password Retriever
MSN Hacker DUC
Head Fuck HotMail HAck
HotMail Hacker XE Edition
HotMail HAck
HotMAil Hacker
MSN Passwords
MSN Flooder
MSN Sniffer
MSN SPY Lite
HotMail Hacker Gold
HotMail HAcker Final
Give me Ur Pass
HotMail Brute Forcer
MSN PAssword Finder
MSN Password Grabber
Hack MSN Password
Hack HotMAil Evolution
MAgic Password Sender
MSN Locker
HotMail Killer
Hot Freeze
MessenPass
HotMAil Hack !
Ice Cold Reload
HotMail Killer 2
Nuke MSN
Yahoo Messenger Login Screen
MSN Messenger 7 Login Screen
MSN Messenger 5 Login Screen
MSN Messenger 4.6 Login Screen
HotMail Login Screen
Fake Web Pages 2
Fake Eeb Pages 1
AOL Killer
Fake Login HotMail
B-S Spy
Saria Fake Logins
Yahoo Password Retrieval
Yacam
Yahoo Cracker
Yahoo Booster
Yahoo Hack!
Yahoo Password Stealer
S-H Yahoo Password Sender
NetWork Password Recovery
NetBIOS Name Scanner
FTP Password Hacker
Cable Modem Sniffer
Port Listening XP
Blue Port Scanner
www 2 IP
XP Killer
Sniff Password
Port Scanner
Fast Resolver
Domain Scan
Whois Domain
NetRes View
PHPbb Defacer
Angry IP Scanner
FTP Brute Forcer
Hook Tool Box
Smart HAck UpLoader
Remote Anything
Post Sage
PHPbb Attacker
Page 6:
Skinner
MSN Bomber Man
Ultimate Nick PopUpz
MSN 7 Universal Patcher
Emoticons Creator
MSN Picture Crawler
Anti Status Bomb
MSN Detector
Multi MSN Loader
Kitle
Protect Lithium
Tray It!
MSN Block Checker
MSN Auto Responder
MSN Virus Cleaner
MSN Dondurucu
Is your windows driving you Nuts ?
Cannot delete file: Access is denied
There has been a sharing violation.
The source or destination file may be in use.
The file is in use by another program or user.
Make sure the disk is not full or write-protected and that the file is not currently in use.
Unlocker is the solution!